Dynamically hide invalid sandbox upgrade parameters based on session permissions to fix the repeated upgrade failure loop for OAI models under All Access.

- Language
- TypeScript
- License
- MIT
- Branch
- main
Install
$ dsh plugin --profile web add github:JUSTMONIKA2022/dsh-sandbox-escalation-fixRun the command above in your terminal to install this plugin via the dsh CLI. You can switch Profile in the top-right corner. New to dsh? Read the beginner tutorial
Install via your agent
Install the DeepSeek Harness plugin JUSTMONIKA2022/dsh-sandbox-escalation-fix for me: review the repository at https://github.com/HakureiMonika/dsh-sandbox-escalation-fix first, then run the install command and verify the plugin loads successfully.
Paste this instruction to the DSH Web GUI assistant — it will install and verify for you.
One-Line Positioning
This is a DSH-compatible plugin that dynamically adjusts model-visible tool parameters and descriptions based on the current Session's sandbox permissions and approval policies, resolving the issue where OAI series models repeatedly trigger sandbox_permissions / justification escalation validation failures and get stuck in retry loops under All Access.
Core Capabilities
- Dynamic Invalid Escalation Field Hiding: Based on the current Session's Sandbox Mode and Approval Policy, remove
sandbox_permissionsandjustificationparameters from the tool Schema that the model should not see - Precise Same-Mode Parameter Normalization: When the model sends a redundant escalation request that exactly matches the current mode, silently delete these parameters and allow the call to proceed as normal; other requests (narrower/wider) remain unchanged
- Synchronized Cleanup of Escalation Hints in Descriptions and Results: Filter out "escalation available" hints that are no longer executable from Shell tool descriptions, file tool results, and
job_output - Monitor Agent/Preset/Tool Lifecycle, Auto Join and Exit Wrapping: No need to rebuild Agent after restriction removal to restore wrapping
- Validate DSH Package Version Consistency at Startup: Avoid runtime behavior inconsistencies from mixed installations
- Collaborate with Other Wrapper Plugins Implementing
dsh.tool-wrapper.v1Protocol: Chain collaboration by priority
Technical Implementation
- Language: TypeScript
- Key Dependencies: @deepseek-ai/cordis, @deepseek-ai/dsh-agent, @deepseek-ai/dsh-sandbox, @deepseek-ai/dsh-sandbox-policy, @deepseek-ai/dsh-tools
- Architecture Pattern: Cordis plugin, registered as
sandbox-escalation-fixnode viacordis.patch.ymlat startup;Supervisorlistens toagent/created,agent/disposed,agent-preset/selected,tools/changeevents, maintains wrapper bindings forbash/pwsh/write/editper Agent, tries collaboration protocolSymbol.for('dsh.tool-wrapper.v1')first, otherwise falls back to ownWrapperBindingregistered toagent.ctx.toolsexact scope - Entry File: src/index.ts (build output lib/index.mjs)
Use Cases
When DSH users use OAI series third-party models (typically like GPT) to execute bash, pwsh, write, edit tools in All Access (danger-full-access + approval=never) or permission boundary Sessions, the model repeatedly sends same-mode/empty justification escalation requests causing tool failures and retry loops. When Code Mode and Native Tool Call show inconsistent behavior, or after Preset dynamically calls agent.ctx.tools.restrict() requiring Agent rebuild to restore wrapping, this plugin uses Schema projection to make these impossible-to-succeed parameters invisible to the model at the request stage, eliminating the cycle from the root.
Prerequisites & Compatibility
| Dependency | Minimum Version | Description |
|---|---|---|
| @deepseek-ai/cordis | 4.0.1 | Plugin runtime |
| @deepseek-ai/dsh-agent / dsh-llm / dsh-sandbox / dsh-sandbox-policy / dsh-scope / dsh-session / dsh-tools / dsh-user-approval | 0.1.0-rc.5, 0.1.0-rc.6, 0.1.0-rc.7, 0.1.0-rc.8, 0.1.1-rc.1 | Must maintain single version within same Profile, enforced at startup |
| @deepseek-ai/schemastery | 3.18.1 | Schema declaration |
| Node.js | ^22.19.0 || >=24.0.0 | engines declaration |
| Platform | Cross-platform | No os/cpu restrictions declared |
Installation
dsh plugin --profile web add --allow-build=dsh-sandbox-escalation-fix github:JUSTMONIKA2022/dsh-sandbox-escalation-fix
Configuration Options
| Config | Type | Description | Default |
|---|---|---|---|
| logLevel | 'silent' | 'info' | 'debug' | Controls plugin's own log output; 'silent' means complete silence, 'info' outputs startup hints and dynamic coordination warnings, 'debug' outputs more detailed coordination process | 'info' |
FAQ
Q: Do I need to modify any configuration after installation?
A: No, this plugin is zero-configuration. Install to the current DSH Profile and restart DSH. The plugin will automatically adjust model-visible tool parameters based on each Session's current Sandbox Mode and Approval Policy.
Q: Does it modify DSH's security validation logic?
A: No. Strict narrow-to-wide checks, approval flows, and one-time authorization semantics remain unchanged. The plugin only does model-visible parameter projection and minimal compatibility handling. It will not automatically approve any escalation requests, nor fill placeholder content for missing or empty justification.
Q: What's the command to uninstall the plugin?
A: Execute dsh plugin --profile <profile> remove dsh-sandbox-escalation-fix in the same Profile used for installation. After uninstallation and DSH restart, original tool behavior is restored, and all wrapper layers are automatically released with the plugin lifecycle.
Q: Do 0.1.1-rc.1 users still need this plugin?
A: Official 0.1.1-rc.1 made partial runtime improvements on the approval=never path, but still uses the same static escalation Schema and validation at execution time. If you still see invalid justification, same-mode danger-full-access errors, or model stuck in retry loops, you can install this plugin to further converge at the Schema level.
Q: When multiple Agents have different permissions, will they affect each other?
A: No. The plugin wraps independently by Agent Exact Scope. Different Sessions, even within the same process, each calculate parameters according to their own permission state without mutual pollution. After permission changes, the next model request's tool Schema will be recalculated immediately based on the new state.
Q: What to do if version error appears at startup?
A: Packages @deepseek-ai/dsh-* within the Profile must maintain consistent versions and must fall within the whitelist: 0.1.0-rc.5, 0.1.0-rc.6, 0.1.0-rc.7, 0.1.0-rc.8, or 0.1.1-rc.1. Mixed or unknown versions will cause the plugin to refuse startup, and the error message will list the actual detected version combination.
Q: What if another plugin also wraps bash/pwsh/write/edit?
A: It depends on whether the other party implements the Symbol.for('dsh.tool-wrapper.v1') collaboration protocol. Those that do can chain collaborate by stable sorting of priority + owner; same-name tool registrations that don't implement it will be explicitly rejected by this plugin to avoid silently changing wrapper order or creating erroneous semantics. In this case, you need to uninstall one of the plugins.
Q: What if escalation fields still appear?
A: Confirm you're viewing the Schema of a Session created after installation (old Sessions use pre-installation tool definitions), and verify via dsh --profile <profile> --dump-config that both the sandbox-escalation-fix layer and Bundle entry exist. If another plugin loaded later replaces the same-name tool, handle it according to the previous question.
Difficulty Level
Beginner — Zero configuration, zero runtime intervention. Install to Profile and restart DSH to take effect. On failure, clear error information is only provided in startup logs or coordination warnings.
Known Issues & Limitations
- Only wraps four built-in tools:
bash,pwsh,write,edit; other tools are not covered - Target tools must satisfy Schema constraints: declare both
sandbox_permissionsandjustificationfields together, or omit both; declaring only one will be rejected at registration - Target tools replaced at runtime with incompatible definitions (missing fields, broken output contract) will only cause the corresponding tool for the corresponding Agent to enter dormancy with a warning logged, without terminating the Host process; after compatible definitions are restored, it will automatically rejoin
- Only supports DSH deployments between
0.1.0-rc.5and0.1.1-rc.1with consistent versions; other versions will refuse to start - When
approvalpolicy isany, all escalation targets are hidden, and the model cannot reach the approval flow (this is existing security semantics, not introduced by this plugin) - No unresolved issues marked as TODO/FIXME found in source code
English | 中文
[!IMPORTANT] This is an independent community plugin. It is not published, maintained, or endorsed by DeepSeek, and it does not modify DeepSeek Harness core packages.
[!CAUTION] DSH rc8 partially improves this issue through an
approval=neverruntime instruction, but tool schemas may still advertise escalation fields that the current Session cannot use, and real-world reliability is not yet clear. RC8 users should first observe the built-in behavior and install this plugin only after reproducing the same-mode escalation, blank justification, or retry-loop failures described below.
dsh-sandbox-escalation-fix is a zero-configuration compatibility plugin that directly resolves the issue of third-party models like GPT failing to call tools such as bash, pwsh, write, and edit under DSH All Access, resulting in repeated retries due to incorrect sandbox escalation parameter prompts.
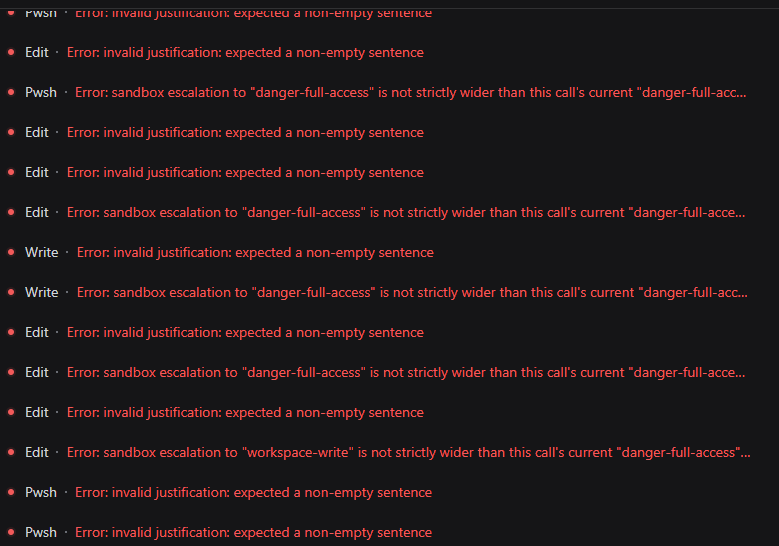
If you've encountered the following errors, this plugin is designed for them:
Error: invalid justification: expected a non-empty sentence
Error: sandbox escalation to "danger-full-access" is not strictly wider than this call's current "danger-full-access" mode
Error: sandbox escalation to "workspace-write" is not strictly wider than this call's current "danger-full-access" mode
Contents
- What It Does
- The Problem It Solves
- Before and After
- Why This Plugin
- This Plugin vs. Execution-Only Normalization
- Compatibility
- Quick Start
- Release One-Click Install and Uninstall
- Upgrade
- Install From GitHub
- Manual Windows Installation
- Behavior at a Glance
- Verify the Fix
- Wrapper Conflicts
- Troubleshooting
- Uninstall
- Development
- License
What It Does
This plugin makes DeepSeek Harness show the model only the sandbox escalation options that the current session can actually use.
In an All Access session (danger-full-access + never), the stock DSH tools still advertise sandbox_permissions and justification on bash, pwsh, write, and edit. But in that state:
- the session is already at the highest sandbox mode, so no wider mode exists;
- the approval policy is
never, so every escalation request is rejected.
When a model fills in those parameters, the call fails before it runs. The model may then retry with different values and get stuck in a loop.
This plugin projects the model-visible tool schema per session, based on the live Sandbox Mode and Approval Policy. It also adds a minimal execution-time fallback for redundant same-mode requests.
The Problem It Solves
- Models still see and send
sandbox_permissions/justificationin All Access sessions, so tools fail before they run. - In
workspace-writesessions, models see two escalation targets even though onlydanger-full-accessis genuinely wider. - With
approval=never, models are still told escalation is possible when every request will be rejected. - Tool descriptions and denial results keep saying “escalation available,” which pushes the model to retry.
- Native Tool Call and Code Mode SDK can show inconsistent capability surfaces.
Why It Happens
DSH tools expose static escalation fields when they are registered, while the modes that can actually be requested depend on each session's current Sandbox Mode and Approval Policy. The original model-visible schema is not projected from that live session state before the request is built, so a model can receive escalation parameters that cannot succeed. Tool validation then rejects those requests before execution, which can start a retry loop.
Before and After
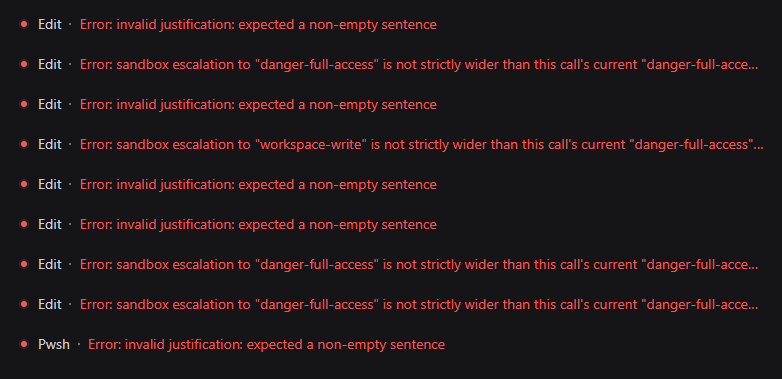
Without the plugin, affected All Access sessions can repeatedly fail before the requested operation runs. The model alternates between an empty justification, a same-mode danger-full-access request, and even a downgrade request that DSH correctly rejects as not strictly wider.
Before: Repeated Validation and Escalation Errors
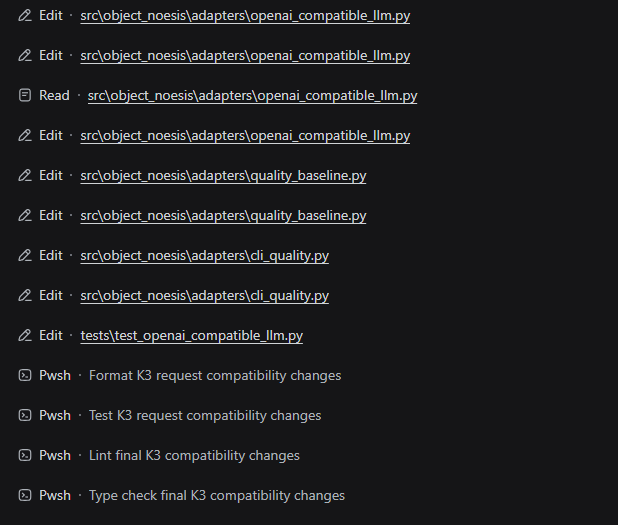
After: Tools Complete the Workflow
After installation, the same model can continue through Edit, Read, Pwsh, formatting, tests, lint, and type checking without entering the invalid escalation loop.
Why This Plugin
It fixes the root cause, not just the error
Some fixes only delete the arguments after the model has already received a broken schema. Calls stop failing, but the model keeps seeing and sending the same unusable parameters.
This plugin projects the model-visible schema from the session's real permission state:
| Current mode | Approval policy | What the model sees |
|---|---|---|
read-only | ask | workspace-write, danger-full-access |
workspace-write | ask | danger-full-access only |
danger-full-access | ask | no escalation fields |
| any mode | never | no escalation fields |
When the model cannot see a parameter that cannot succeed, it stops reaching for it.
It won't fix Native Tool Call but leave Code Mode broken
Projection happens on the tool definition inside each Agent Exact Scope, so Native tool schemas and the Code Mode SDK read the same result:
- Native tool schemas omit impossible escalation fields;
- Code Mode TypeScript/Python SDKs omit them too;
- behavior stays identical across both modes.
It won't silently swallow a downgrade request
The execution fallback is deliberately narrow: it removes sandbox_permissions and justification only when requestedMode === effectiveMode, treating that pair as an idempotent duplicate.
Downgrade or invalid requests are left untouched and go through normal DSH validation:
danger-full-access+ requestdanger-full-access→ ignored, tool runs normally;danger-full-access+ requestworkspace-write→ not executed as Full access;read-only+ a wider request → enters the normal approval flow.
It will not trade a clear error for silently running a call with broader access than the caller asked for.
It won't invent an approval reason
For genuine escalation requests, the plugin does not fill in a fake or placeholder justification. Missing, blank, or invalid reasons still go through DSH's own validation, so the approval flow sees honest, auditable input.
It won't say “don't escalate” while results say “escalation available”
When the session has no viable escalation target, the plugin also cleans up the natural-language side:
- the escalation guidance tail is removed from Shell tool descriptions;
- impossible
escalation availablehints are removed from Shell, filesystem, Code Mode, andjob_outputresults.
The model no longer receives contradictory instructions from the parameter schema, the description, and the failure output.
It won't modify or bypass DSH's security core
approveEscalation() keeps its strictly-wider check, approval flow, and one-shot authorization semantics. The plugin only projects the model-visible surface and removes one redundant same-mode pair before delegating:
- no removal of the strictly-wider check;
- no auto-approval when
approval=never; - no extra permissions;
- no changes to DSH installation or core packages.
It won't treat every session the same
Wrapping happens per Agent/Session, never on the global tool registry. In the same process:
Session A = read-only + ask              → sees two escalation targets
Session B = danger-full-access + never   → sees no escalation fields
Each session is independent. If a session switches permission state mid-flight, the next model request gets a freshly projected schema.
It won't leave stale wrappers behind
The plugin listens to Agent creation, disposal, Preset changes, restrictions, and tool changes. When a dynamic Preset calls agent.ctx.tools.restrict(), the corresponding Exact Scope wrappers disappear synchronously with the restricted parent tools. Lifting the restriction restores the projected wrappers; tools absent during Agent creation are wrapped when they later become visible. Each Agent is coordinated independently, and disposed Agents or unloaded plugins restore the original definitions.
It won't lock you to a single DSH release
The plugin supports DSH 0.1.0-rc.5, 0.1.0-rc.6, 0.1.0-rc.7, and 0.1.0-rc.8. At startup it verifies that the installed @deepseek-ai/dsh-* packages are consistent and supported. Incompatible tool definitions fail explicitly instead of producing silent misbehavior.
It won't add configuration burden
Zero configuration. Install it into the Profile you actually use and start DSH as before. The test suite contains 28 tests built on real DSH packages, covering schema projection, Code Mode SDK generation, dynamic restrictions, multi-Agent isolation, delegate and wrapper-protocol replacement, internal timeout-budget forwarding, failure-hint cleanup, and unload behavior.
This Plugin vs. Execution-Only Normalization
| Capability | This plugin | Execution-only normalization |
|---|---|---|
| Hide impossible escalation fields from Native tools | yes, per session | no |
| Hide the same fields from the Code Mode SDK | yes, from the same exact-scope definition | no |
| Remove only an exact same-mode redundant request | yes | implementation-dependent |
| Preserve explicit downgrade and invalid requests for DSH validation | yes | not guaranteed |
Preserve missing or blank justification for DSH validation | yes | not guaranteed |
| Remove impossible advice from descriptions and results | Shell, FS, Code Mode, and job_output | no |
| React to Agent, Preset, and tool lifecycle changes | yes | implementation-dependent |
Compatibility
- Node.js
^22.19.0or>=24.0.0 @deepseek-ai/dsh-*0.1.0-rc.5,0.1.0-rc.6,0.1.0-rc.7, or0.1.0-rc.8@deepseek-ai/cordis4.0.1
The plugin checks the installed DSH package versions at startup. Mixed rc.5/rc.6/rc.7/rc.8 installations and unknown DSH versions fail explicitly. An initially visible target with partial escalation fields or an incompatible output definition rejects that Agent's registration; a target that omits both escalation fields is accepted as already safe. During runtime, a Preset restriction or stable provider removal makes the wrapper dormant, while an incompatible replacement is isolated to that Agent and target tool and reported without terminating the Host process. A later compatible definition is wrapped automatically.
Quick Start
The plugin is a zero-configuration fix. Install it into the Profile that runs the affected sessions, then start DSH normally:
dsh --profile <profile>
You do not need to change the model configuration, Sandbox Mode, Approval Policy, or Agent Preset. The plugin projects the model-visible parameters from each Session's current permission state.
Release One-Click Install and Uninstall
The 0.1.2 Release uses the DSH CLI, so no manual Profile patch editing is required. Download and extract dsh-sandbox-escalation-fix-release.zip; it contains the tarball, one-click install and uninstall scripts, and a concise Chinese usage guide.
Close DSH before installing or removing the plugin. Ensure that dsh is available on PATH and that the running DSH version is rc5, rc6, rc7, or rc8. RC8 users should install only after reproducing the affected behavior.
Install into the default Web Profile
powershell -NoProfile -ExecutionPolicy Bypass -File ".\install-release.ps1"
The script runs dsh plugin --profile web add <tgz-absolute-path>.
Install or remove another Profile
For example, use headless instead of the default web Profile:
powershell -NoProfile -ExecutionPolicy Bypass -File ".\install-release.ps1" -Profile headless
powershell -NoProfile -ExecutionPolicy Bypass -File ".\uninstall-release.ps1" -Profile headless
Remove from the default Web Profile
powershell -NoProfile -ExecutionPolicy Bypass -File ".\uninstall-release.ps1"
The removal script runs dsh plugin --profile web remove dsh-sandbox-escalation-fix. Restart DSH after installation or removal.
Build the Release ZIP
powershell -NoProfile -ExecutionPolicy Bypass -File ".\build-release.ps1"
The script builds lib, packages the npm tarball, then creates dsh-sandbox-escalation-fix-release.zip in release/. The generated directory is ignored by Git; upload only this ZIP as the GitHub Release asset.
Upgrade
Close DSH before upgrading. The plugin package name, Bundle ID, and Profile patch row are unchanged, so an existing installation does not need another cordis.patch.yml entry.
GitHub Commit Installation
Run the same installation command with the new reviewed commit SHA:
dsh plugin --profile <profile> add github:<owner>/dsh-sandbox-escalation-fix#<new-commit-sha>
This updates the Profile dependency and rebuilds the package. Keep the existing allowBuilds entry when pnpm requires it, inspect --dump-config, then restart DSH.
Manual Web Profile Installation
Use the repository or packaged source that contains the new built lib directory. Open Windows PowerShell in that plugin directory and run:
powershell -NoProfile -ExecutionPolicy Bypass -File ".\deploy-web-profile.ps1"
The script uses $DSH_HOME when set, otherwise %USERPROFILE%\.dsh. It replaces only the eight published lib artifacts, compares every SHA-256 hash, and prints Deployment verified. only when the installed Web Profile exactly matches the new build. It does not modify the Profile patch or copy node_modules. Restart DSH after verification.
Install From GitHub
Install into the exact Profile that runs the affected sessions. Pin a reviewed commit SHA, because a Git dependency executes this package's prepare script during installation:
dsh plugin --profile <profile> add github:<owner>/dsh-sandbox-escalation-fix#<commit-sha>
pnpm 10 blocks Git dependency build scripts until the Profile explicitly allows them. If the first installation reports a blocked build, add this entry to $DSH_HOME/profiles/<profile>/pnpm-workspace.yaml:
allowBuilds:
  dsh-sandbox-escalation-fix: true
Run the installation command again, then inspect the composed configuration:
dsh --profile <profile> --dump-config
The output should contain a dsh-sandbox-escalation-fix bundle layer and the sandbox-escalation-fix plugin row. Start DSH normally after verification:
dsh --profile <profile>
Manual Windows Installation
A detailed Windows walkthrough — Profile paths, folder layout, nested node_modules, and the correct replacement for an empty [] patch — is available in README.zh.md.
For a compact file-by-file walkthrough, see Tutorials that even Peppa Pig can understand. The original Chinese layout is preserved in 奶龙也能看懂的食用说明.txt.
The minimum manual layout is:
<profile-directory>\
├── cordis.patch.yml
└── node_modules\
    └── dsh-sandbox-escalation-fix\
        ├── package.json
        ├── cordis.patch.yml
        ├── README.md
        ├── README.zh.md
        └── lib\
            ├── index.mjs
            ├── index.d.mts
            ├── wrapper-protocol.mjs
            └── wrapper-protocol.d.mts
Merge this block into the Profile's cordis.patch.yml; do not overwrite unrelated Profile patches:
- insert:
    - id: sandbox-escalation-fix
      name: dsh-sandbox-escalation-fix
Do not copy this repository's node_modules into the Profile. Multiple Cordis or DSH module instances can break Scope and Service identity.
To update an existing installation, follow Upgrade; do not repeat the Profile patch step.
Behavior at a Glance
| Scenario | Plugin behavior |
|---|---|
danger-full-access, or any mode with never | Model sees no sandbox_permissions / justification |
workspace-write with approval allowed | Only danger-full-access is advertised |
read-only with approval allowed | workspace-write and danger-full-access are advertised |
| Model sends the exact current mode as an escalation request | The redundant pair is removed, then the original tool runs |
| Downgrade, unknown target, unpaired arguments, genuine escalation | Left untouched for original DSH validation |
| No viable escalation target | Shell description escalation tail is removed; impossible hints are stripped from denial results |
| A dynamic Preset restricts a target tool | Its Exact Scope wrapper disappears in the same synchronous change |
| The restriction is lifted or the provider returns | The projected wrapper is restored automatically |
| A runtime replacement is incompatible | Only that Agent and target remain unwrapped until a compatible definition appears |
Verify the Fix
After installing or updating the plugin, fully restart DSH and create a new session.
A successful Web startup proves that the Profile composes and the plugin loads without a process-level failure. For a source checkout, this command starts the Web profile directly:
node --import tsx/esm apps/cli/src/bin.ts web
Run it with a supported Node.js version available on PATH. Wait for dsh web: http://127.0.0.1:3080, then perform the behavior checks below. Startup alone does not prove dynamic restriction behavior.
- Select the previously affected OAI model.
- Set Access Mode to All Access.
- Ask the model to run
pwshand print the current directory. - Ask it to create a temporary file with
write. - Ask it to update the file with
edit, then read it back. - Switch workspaces and open existing sessions to confirm normal session restoration.
- If the Preset uses
agent.ctx.tools.restrict(), enter its restricted state and confirm hidden tools disappear; lift the restriction and confirm they return without recreating the Agent.
The calls should complete without sandbox_permissions argument errors or impossible escalation advice. Existing sessions should remain visible, workspace switching should work, and new sessions should be created in the selected workspace. The complete manual acceptance checklist is in README.zh.md.
Wrapper Conflicts
The plugin owns the bash, pwsh, write, and edit names inside each Agent Exact Scope. Another plugin may share those names only through the explicit Symbol.for('dsh.tool-wrapper.v1') protocol. Cooperative layers are ordered by priority and owner.
An unknown same-name wrapper causes Agent registration to fail explicitly. In that case, remove one of the conflicting plugins rather than relying on an undefined load order.
Protocol types are exported from:
import {
  TOOL_WRAPPER_PROTOCOL,
  type WrapperLayer,
  type ToolWrapperProtocolV1,
} from 'dsh-sandbox-escalation-fix/wrapper-protocol'
Troubleshooting
| Problem | What to do |
|---|---|
| The plugin does not load | Confirm installation and startup use the same --profile, then inspect --dump-config |
| A Git install cannot build | Add the package to the Profile's allowBuilds map and retry the installation |
| Startup rejects DSH versions | Keep the relevant @deepseek-ai/dsh-* packages on one supported release candidate |
| Agent registration reports a tool conflict | Remove the incompatible same-name wrapper or update it to implement the wrapper protocol |
| A dynamic Preset hides tools | This is expected; the plugin mirrors tools.restrict() and restores wrappers when the restriction is lifted |
| A runtime reconciliation warning appears | Check the named target's replacement definition; other tools and Agents remain active while the plugin waits for a compatible definition |
| Escalation fields remain visible | Test a new session and check whether a later plugin replaces the same tool names |
| Manual installation breaks Scope behavior | Remove the plugin's nested node_modules and verify that package.json is directly under the expected package directory |
Uninstall
dsh plugin --profile <profile> remove dsh-sandbox-escalation-fix
The plugin lifecycle removes its wrapper hosts, wrapper layers, and result filters. Confirm that --dump-config no longer lists the bundle after removal.
Development
npm install
npm test
npm run build
npm pack --dry-run
Git installation builds from source through the self-contained prepare script. Registry or tarball distribution may ship the generated lib files instead.
License
Read the usage guide →
Install steps, key points, FAQ and compatibility for this plugin — auto-derived from indexed fields.
Listing badge

[](https://deepseek-plugin.org/plugins/JUSTMONIKA2022/dsh-sandbox-escalation-fix)Paste this markdown into your GitHub README to link back to this listing. The badge only states the listing — not a security endorsement.